AI Red Teaming
See your environment the way an AI-enabled adversary does
AI changes what attackers can reach, how they identify targets, and how fast they can move from access to impact. We test your defenses against those techniques and evaluate the AI systems they target: models, pipelines, and the infrastructure connecting them.
Trusted in AI security
As red team of record for multiple frontier AI companies, a participant in OpenAI’s Daybreak program and one of the few organizations that can access and deliver services using Daybreak Red, our practitioners operate at the leading edge of AI-enabled adversary simulation. That expertise directly informs our approach to AI-assisted offensive security and tool development. We also partner with the UK’s AI Security Institute (AISI) to evaluate frontier model capabilities.
The SpecterOps difference

Access to impact
The security concern is blast radius: what a compromised AI system can reach, and how fast an AI-enabled adversary can move through it.

Full lifecycle coverage
We assess AI systems at every stage, from design through production. Finding a vulnerability before release means fixing issues on your terms.

Attack path expertise
Mapping chains of abusable conditions is foundational to our practice. We apply that methodology to AI pipelines, tracing how initial access enables environment-wide pivot.

Ahead of the threat
Engagements with frontier AI companies, including OpenAI’s Trusted Access for Cyber program, keep our understanding of AI attack surfaces ahead of the threat landscape.

Test and exercise
A playbook never exercised is just a hypothesis. We run red team operations against production AI systems and structured exercises that build lasting response capability.

Leading adversarial discovery
Our practitioners are at the front lines of adversarial discovery. BloodHound, Certified Pre-Owned, SCCM research, and GhostWorks make up our track record.
RED TEAM OPERATIONS
Red teaming your full environment
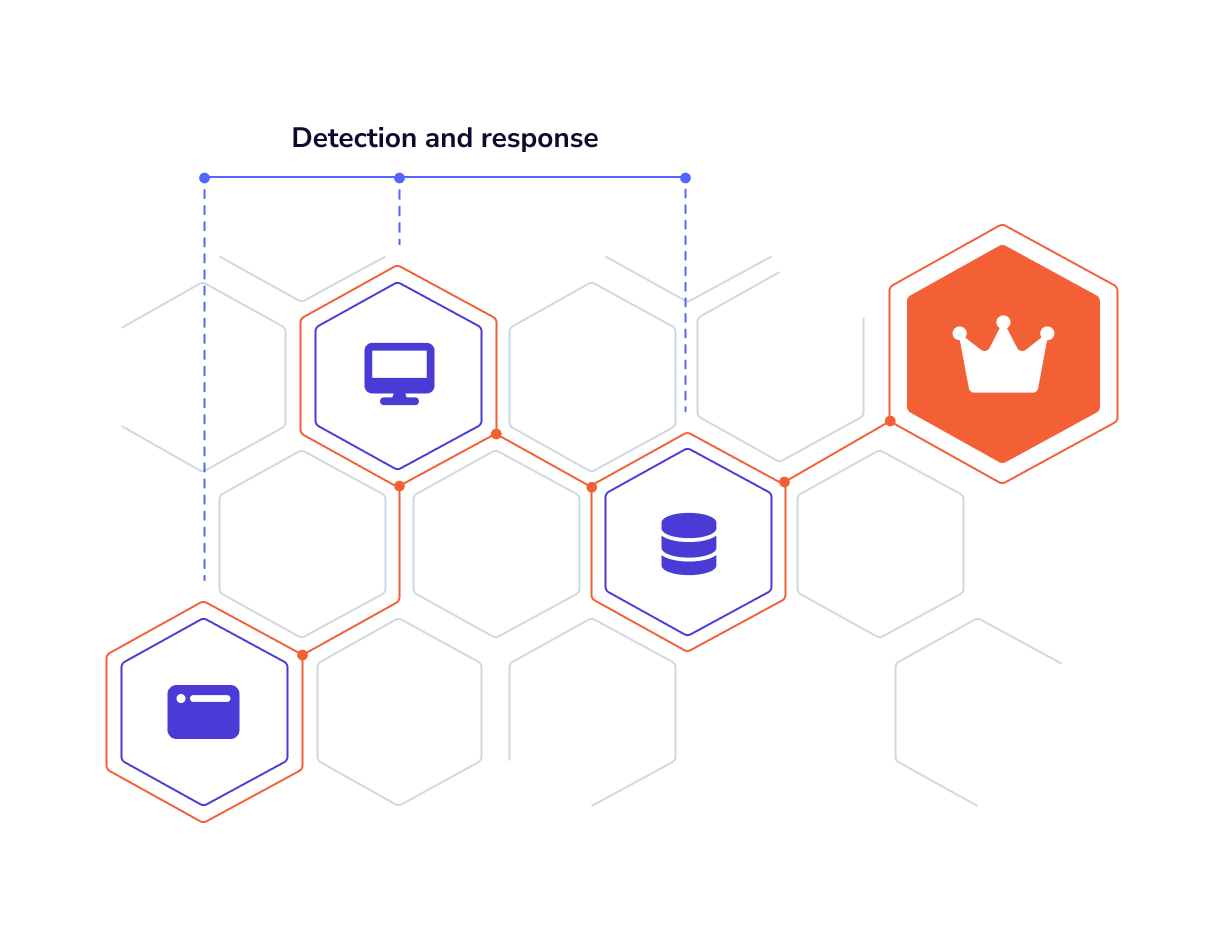
We also run red team exercises against traditional infrastructure, scoped to your priorities and built to strengthen detection and response, not just surface gaps. Your team practices against worst-case scenarios without worst-case risk, closes gaps in detection technology, investigation processes, and staff readiness, and walks away with institutional knowledge that holds between engagements. Collaborative debriefs provide the context to keep improving.
Inside an engagement
Our AI red team assessments cover the full stack, from model behavior under adversarial conditions to supporting infrastructure, including adversary simulation exercises that emulate AI-enabled threat actor techniques.
Engagements span design through production and include threat modeling, direct model inference assessments, penetration testing, and red team operations run against production systems. Each concludes with a written report and out brief presentation for your team.
AI red teaming is part of AI Adversary Operations, which also includes AI Red Team Enablement and Cyber Ranges for AI Evaluations.
AI security testing that goes beyond the model
Standard security testing wasn’t built to find AI-specific vulnerabilities. And most AI-focused assessments ignore both the attack paths connecting the model to your broader environment and the adversaries now using AI to exploit them.
AI did not make least privilege or deny-by-default less important. It made ignoring them more dangerous. A misconfigured AI system doesn’t just create exposure; it can act on it, across every system it can reach.
We evaluate the full stack: Model behavior under adversarial conditions, non-human identity controls, API integration points, and supporting infrastructure, each assessed from the perspective of a compromised user against objectives tied to actual business risk. That coverage extends into production, with red team exercises that simulate AI-enabled adversary techniques against live systems to test whether detection and response hold up.
We use AI tooling across our engagements to accelerate vulnerability discovery, zero-day identification, and attack path analysis, informed by the same adversary expertise behind our industry-recognized research and tooling.
Getting started
Every engagement starts with a conversation about your environment and what you're trying to protect. Contact us to have that conversation.