Services & Tradecraft
Defend against advanced threats with adversary expertise and AI-enabled offensive security
We test your defenses from the perspective of AI-enabled adversaries and build the capabilities to help you respond. From offensive engagements that expose critical risks to maturity assessments and program development that build lasting capabilities, we partner with you to harden defenses across traditional infrastructure and AI systems.
Deep expertise. Proven methodology.
We’re the foremost experts in adversary tactics and exploitation techniques, with proven methodologies refined through thousands of engagements across the most security-conscious organizations in the world, including Fortune 500 companies, government agencies, and defense programs.
It’s our mission to create a more secure world by demystifying adversary tradecraft and promoting actionable approaches accessible to all.

200
+
Enterprise and government customers
10,000
+
Practitioners trained
400
+
Community contributions and over 100 open-source tools
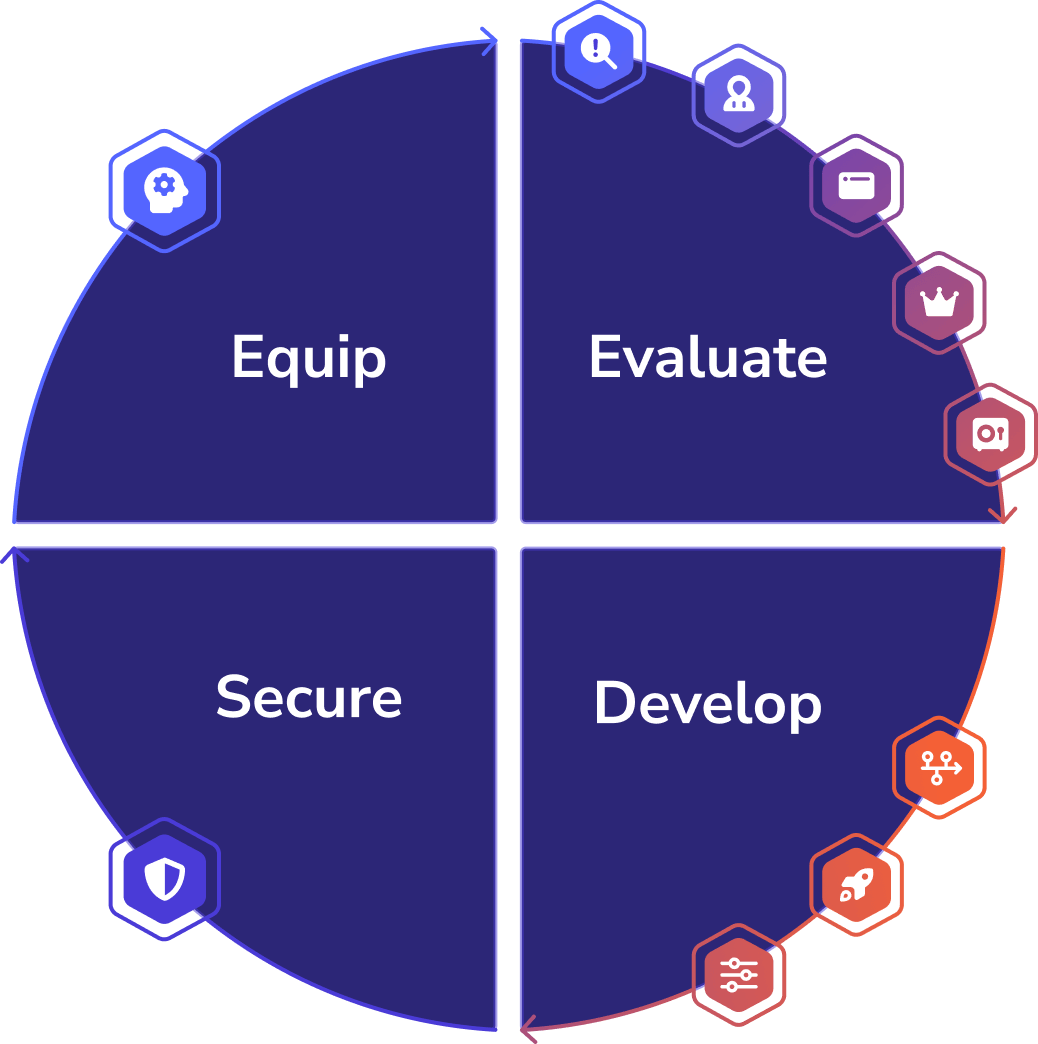
How we partner with you

Evaluate
Expose real-world risk through offensive engagements that test your environment the way modern, AI-enabled adversaries attack.

Develop
Build and mature defensible security operations and programs with documented processes, clear roadmaps, and capabilities your team owns independently.

Equip
Train your people in adversary tactics through hands-on courses and realistic environments designed by front-line practitioners. Explore training.

Secure
Continuously identify and eliminate identity attack paths to your most critical assets with BloodHound Enterprise. Build, scale, and mature your Attack Path Management practice with expert guidance through BloodHound Scentry.
AI red teaming
AI has changed offensive tradecraft, accelerating what adversaries can execute and at what scale.
Our red team brings deep adversary expertise and leading-edge AI tooling and tradecraft to simulate that behavior against your environment, replicating how AI-enabled adversaries operate and testing whether your defenses hold up. We test both traditional infrastructure and AI systems, because adversaries don’t distinguish between them.
As red team of record for multiple frontier AI companies and a partner on OpenAI’s Daybreak program, our practitioners operate at the frontier of AI security. That includes access to and the ability to deliver services with Daybreak Red, directly informing our approach to AI-assisted threat simulation research and tool development, including Sage, an AI-powered virtual agent for Mythic command and control.
All red team exercises are built to develop lasting capability:
- Practice response against worst-case scenarios without worst-case security risk
- Close gaps in detection technology, investigation processes, and staff readiness
- Receive collaborative debriefs with context to improve future response
- Build institutional knowledge that strengthens your team between engagements
Operating at the frontier
We serve as red team of record for multiple frontier AI companies
Access to Daybreak Red
We have access to and can deliver services with OpenAI’s Daybreak Red
Full lifecycle coverage
We assess AI systems at every stage, from design through production
Defining the field
GhostWorks, Blacklight, Sage, and AI adversary research shaping the industry
AI security assessments
AI systems introduce unique attack surfaces across models, pipelines, and supporting infrastructure. Adversaries are already exploiting them. We evaluate these systems across every stage of the lifecycle, breaking them down into individual components to identify vulnerabilities unique to AI alongside traditional infrastructure risks.
Evaluations across design and development stages
Infrastructure assessments from the perspective of a compromised user
Offensive testing of production AI systems, including model behavior and agentic workflows
Application security assessments
We assess web applications, desktop applications, AI systems, and AI models for exploitable vulnerabilities, with findings focused on demonstrable real-world impact. Our practitioners use AI tooling to accelerate vulnerability discovery and attack path analysis, backed by the deep adversary expertise to know what matters.
Findings focused on exploitable vulnerabilities with real impact, not noise
Assess from both authenticated and unauthenticated perspectives, including multi-role and multi-tenant testing
Deliver actionable remediation guidance with demonstrated impact on critical data
Evaluate AI systems and models for adversarial vulnerabilities alongside traditional application risks
Penetration testing
We’ll work with you to define the objectives that matter most, focusing on viable attack paths to your most sensitive data and management systems across network, application, AI, and specialty environments. Our practitioners take an objective-driven approach, combining AI tooling and deep adversary expertise to find more within a single engagement, accelerating attack path analysis and uncovering the ‘unknown unknowns’ that time constraints typically prevent.
Every finding tied to real-world impact and translated into business risk
Independent, third-party perspective from operators who know the adversary’s playbook
Evidence-based justification for security investments
Build and sustain security operations
Assessments reveal where you stand. Our program development services and maturity assessments help you build the teams, processes, and institutional knowledge that help you stay ahead of threats.
Attack path assessments
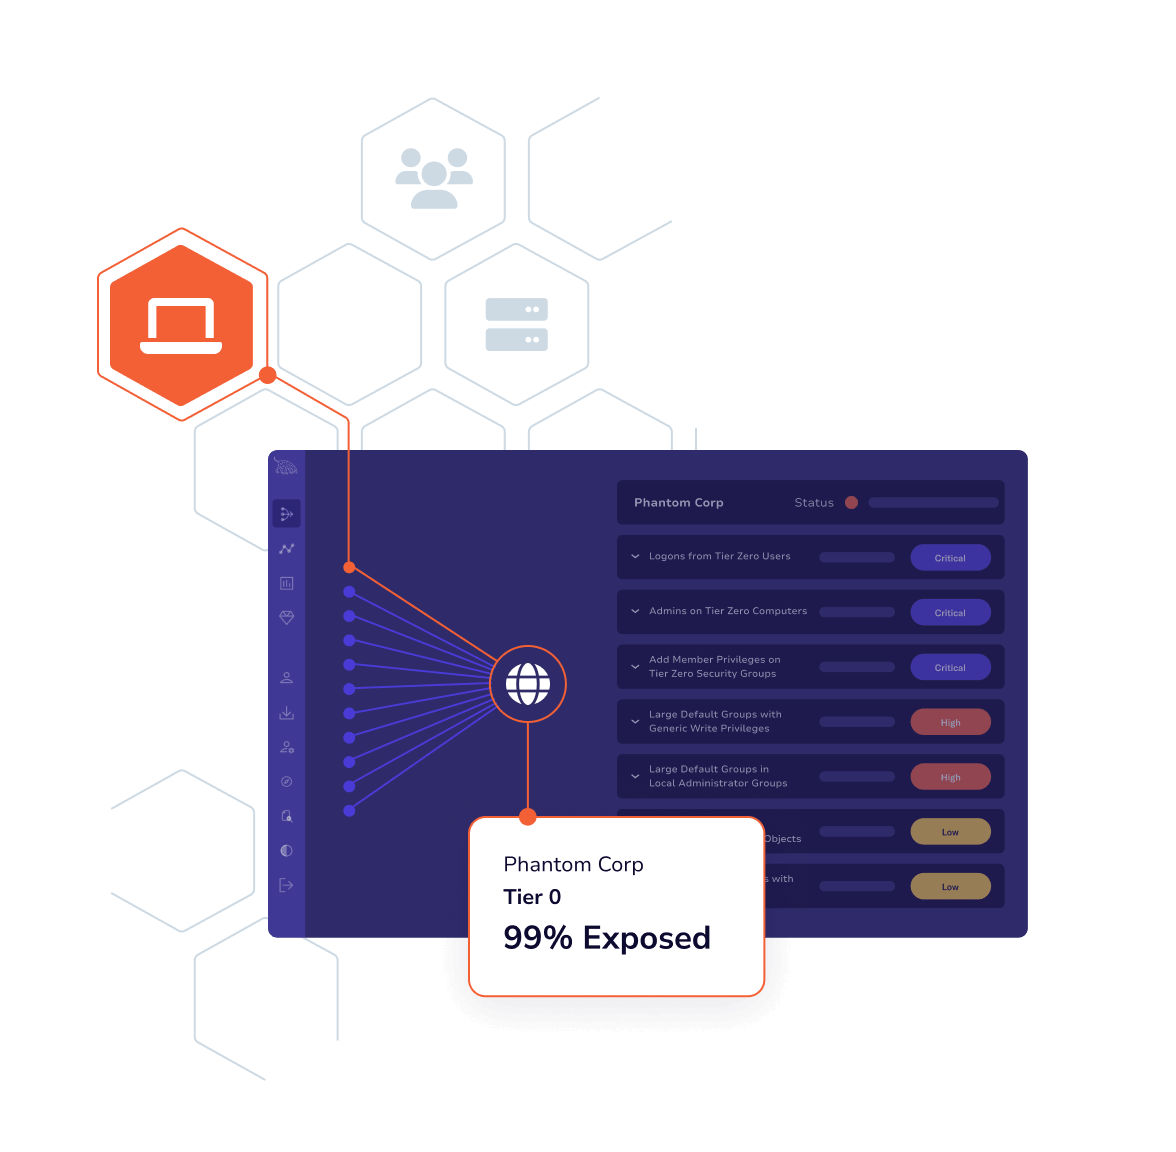
Powered by BloodHound Enterprise, we comprehensively map chains of abusable privileges across critical assets to identify choke points in your identity attack surface.
Evaluate attack paths at scale across AD, Entra ID, GitHub, Okta, and JAMF
Eliminate thousands of exposures at critical choke points through prioritized remediations
Demonstrate measurable risk reduction to boards and auditors
Maturity assessments
We’ll establish a defensible baseline and deliver a clear roadmap for measurable improvement.
Assess people, processes, and technology across your security operations program
Prioritize improvements that drive the greatest security impact
Provide evidence of due diligence and measurable progress over time
Purple team assessments
Working alongside your team, we evaluate preventative and detective controls using comprehensive test cases that represent real attack variations.
Our layered testing model exposes where detection logic breaks down against real adversary behavior
Build institutional knowledge that strengthens your team’s detection capabilities
Develop repeatable validation methodologies your team can sustain
Custom security solutions
We partner with you to build robust prevention, detection, validation, and response capabilities across defensive and offensive operations. Not every security challenge fits a standard engagement, and we bring the same elite offensive security expertise and adversary mindset to unique and emerging technology challenges. Custom assessments and advisory services deliver actionable outcomes, knowledge transfer, and measurable security improvements.
Stand up red team, purple team, threat hunting, detection, or AI red team programs
Develop attainable goals, effective metrics, and documented processes
Build programs designed for sustained capabilities and organizational ownership, not consultant dependence
Advancing AI security
As AI systems become critical infrastructure, they become targets. We bring the same adversary expertise that defines our services to the challenge of securing AI systems, from model evaluations and infrastructure assessments to enterprise-scale Cyber Ranges for AI used by the AI Security Institute (AISI) to evaluate frontier model capabilities. See AISI’s “Measuring AI Agents’ Progress on Multi-Step Cyber Attack Scenarios” research.
We are the red team of record for multiple frontier AI companies and participate in OpenAI’s Daybreak program, working alongside leading security firms and Fortune 500 enterprises to push the frontier of AI-enabled cyber defense.
What sets us apart
Adversary tradecraft expertise
Our services are built on deep understanding of how adversaries operate, including how AI is changing offensive tradecraft, not compliance frameworks or theoretical risk models.
Built and delivered by operators
The same people who publish the original research and build the tools we’re known for are the ones executing your engagements.
Capabilities you own
We build programs your team sustains independently. Every engagement includes knowledge transfer, documented processes, and leave-behind methodologies.
Measurable outcomes
Actionable findings tied to real-world risk, with clear remediation guidance and steps to reproduce that demonstrate security posture improvement.
Research that shapes the industry
Our team publishes original research like Certified Pre-Owned, NTLM Relay Attacks, and SCCM adversary tradecraft, and develops AI security tooling including Blacklight, an open-source toolkit for assessing AI agent attack surfaces on endpoints, and is researching the use of LLMs to autonomously generate Mythic C2 agents from prompt to deployment. We regularly present at Black Hat, DEF CON, Troopers, x33fcon, ShmooCon, and BSides. This commitment to advancing the security community shapes how the industry understands and defends against adversary tradecraft.
Ready to close the gap?
Whether you need to validate your defenses, build your team's capabilities, or understand how adversaries see your environment, we're ready to partner with you.