AI adversary operations for the enterprise
Frontier AI models, agentic identities, and AI-enabled attacks are fundamentally altering enterprise security. As timelines shrink, resilience depends on understanding your AI attack surface and AI red teaming it the way an adversary would. SpecterOps AI Adversary Operations is built to help enterprise organizations stay ahead of the risks posed by AI-enabled adversaries.
Advancing cyberdefense with frontier AI models
AI red teaming
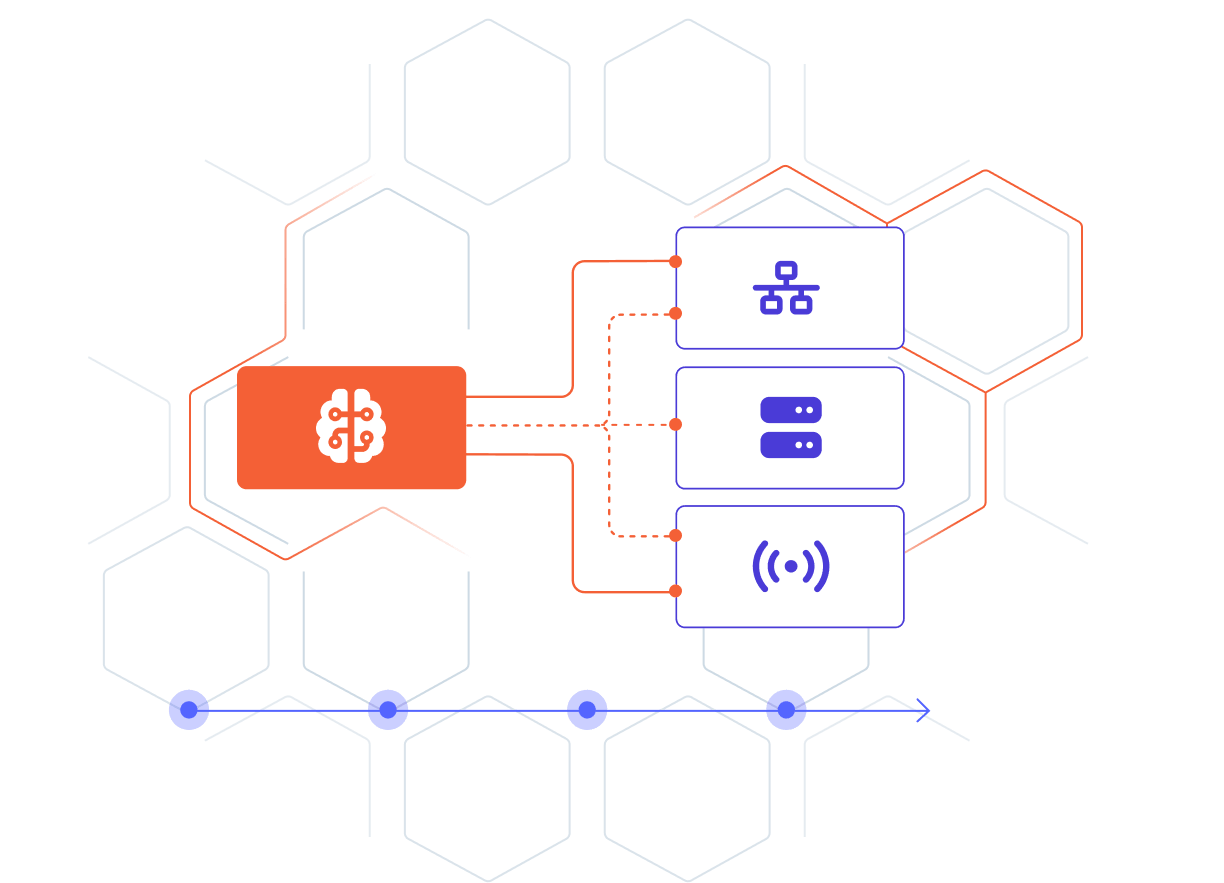
Standard security testing was not built to find AI-specific vulnerabilities, and most AI assessments ignore the attack paths connecting the model to your broader environment. We evaluate the full stack: model behavior under adversarial conditions, non-human identity controls, API integration points, and supporting infrastructure, each assessed from the perspective of a compromised user against objectives tied to real business risk. Red team exercises extend that coverage into production, simulating AI-enabled adversary techniques against live systems.
Listen to Russel Van Tuyl on Soap Box: Red teaming AI systems with SpecterOps.
AI red team enablement
Adversaries use AI to spin up tooling tailored to one target, faster than signature-based detection can follow. We test against those techniques and evaluate the AI systems they target: model behavior under adversarial conditions, non-human identity controls, API integration points, and supporting infrastructure, assessed against real business risk. AI Red Team Enablement builds that hands-on fluency inside your team, with open-source red team infrastructure tooling, AI skill packages carrying practitioner context, and on-demand, expert-led training.
Cyber ranges built for enterprise AI
As AI models grow more sophisticated, governments and enterprises need rigorous environments to test model capabilities for both blue teams and red teams.SpecterOps delivers enterprise-scale cyber ranges for AI that provide standardized evaluation environments with known completion paths combined with the realism necessary to validate AI model capabilities under production-like conditions. Designed by leading offensive security experts, our ranges deliver the complexity and scale necessary for rigorous assessment.
AI identity attack path management
110 million identities. Five billion trust relationships. 650 billion attack paths. Attack paths are exponential to identities, and agentic AI is exploding the identity landscape. It’s not enough to answer “who has intended access.” Defenders need to know what happens when that access is abused.
BloodHound Enterprise continuously maps how effective privilege forms across hybrid human-machine environments, identifies choke points that enable escalation, and removes the most critical paths before they can be abused.
Related resources

Trends in APM 2026
Explore how AI is impacting budgets, priorities, and technology adoption for defenders.