Report

AI Security Starts With Eliminating Attack Paths

AI-enabled attackers can move from foothold to impact in minutes, using access your environment already grants. This report shows security leaders why cutting identity attack paths is the most urgent step in AI security, and how to find the choke points where one fix removes thousands of paths.

Key Takeaways

  • Every AI agent runs as an identity, and it inherits the identity tech debt already present in your environment.
  • Attack paths grow exponentially with identity sprawl. An organization with 40,000 identities can carry more than 750 million paths.
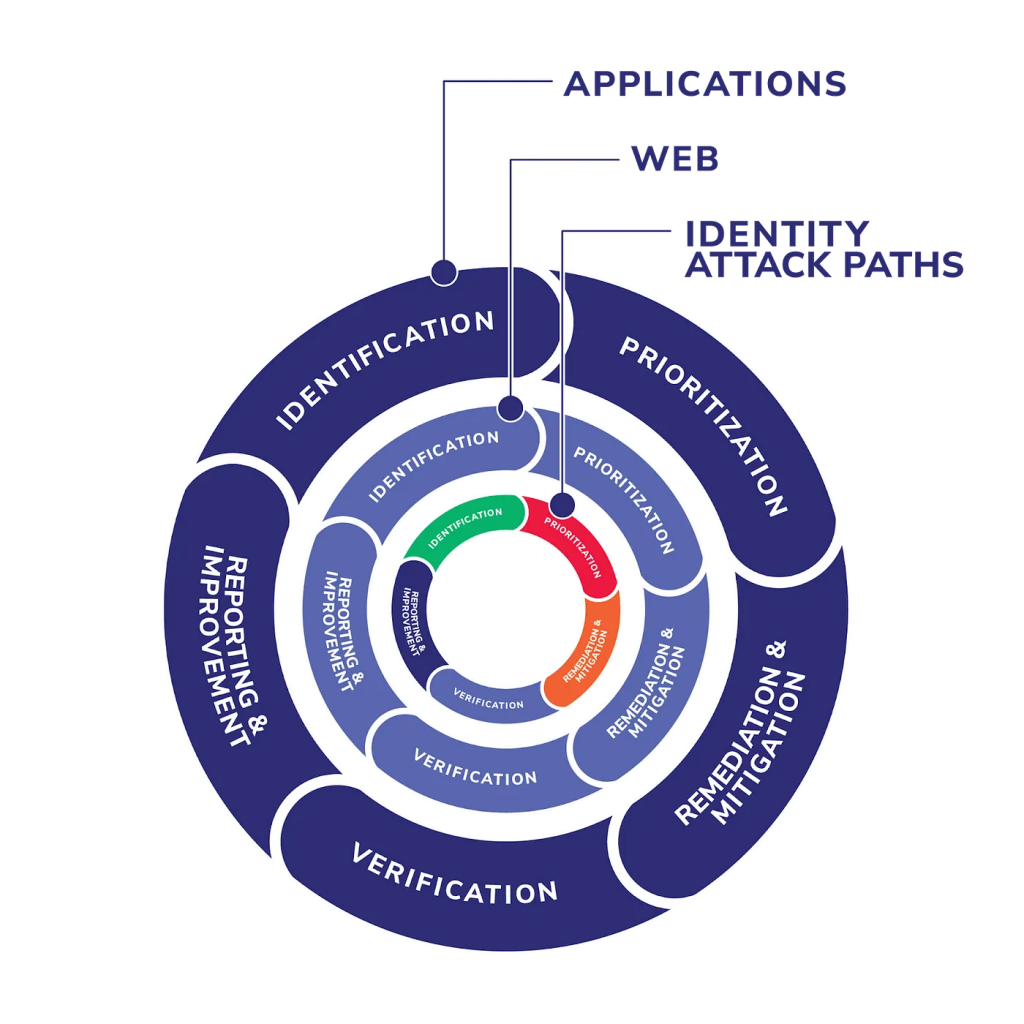
  • Identity governance, PAM, ITDR and CTEM each see part of a path. Attack Path Management maps the whole route across Entra ID, Okta, AWS, GitHub and Active Directory.
  • Fixing choke points removes thousands of paths at once. BloodHound Enterprise customers cut attack paths by 54% within six months.
Estimated read time: 12 minutes

Executive Summary

Enterprises are putting AI agents to work fast: 88% of large-enterprise security leaders already use them or plan to within the next 12 to 18 months. Every agent runs as an identity, and it inherits the access debt already in your environment. The median SpecterOps customer environment holds 58 million attack paths, which are chains of legitimate permissions that connect an ordinary foothold to critical systems. AI-enabled attackers can find and use those paths in hours, without any novel exploit.

Patching never touches these paths, and access reviews miss them because each permission passes review on its own. This report shows how Attack Path Management maps the full route across platforms and finds the choke points where one fix removes thousands of paths. BloodHound Enterprise customers cut attack paths by 54% within six months.